Seamlessly Implement Powerful Distributed Tracing with OpenTelemetry and Send Insights to Azure Application Insights
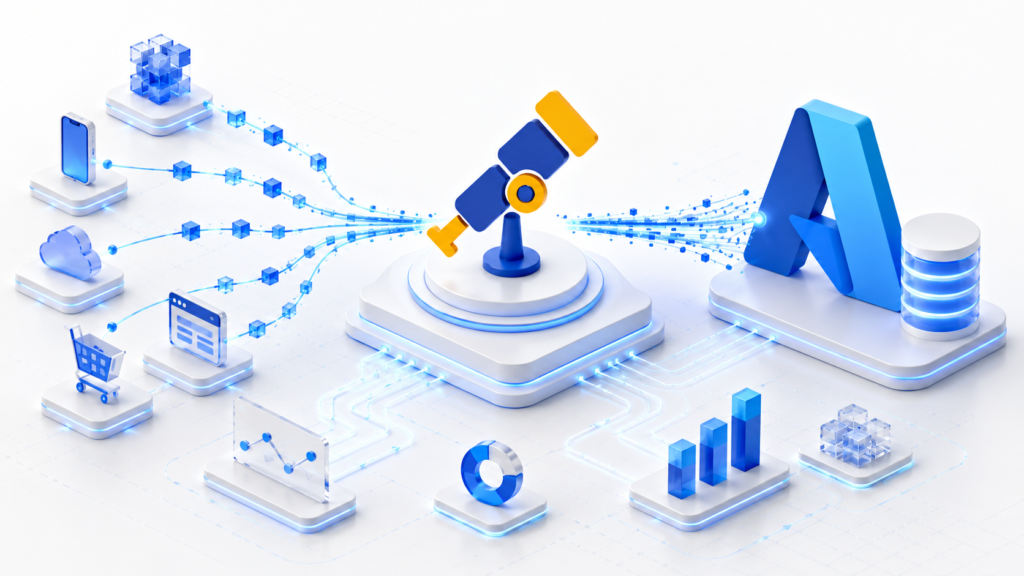
In modern distributed systems and cloud-native applications, understanding how requests flow through services is critical for maintaining performance, reliability, and debuggability. Traditional logging alone often falls short when it comes to tracking issues across multiple components or services. This is where tracing becomes essential. Tracing provides end-to-end visibility into the lifecycle of a request as […]
Automating Security Testing in CI/CD Pipelines: Best Practices and Essential Tools
As companies drive code more quickly than ever, embedding security at the beginning of the development process referred to as “shift-left security” has become essential. Automating security tests within CI/CD pipelines guarantees vulnerabilities get detected early, compliance is ensured, and risk is reduced without hindering delivery. What is Automated Security Testing in CI/CD Pipelines? Security […]
Setting Up Azure Hub-Spoke Architecture with VNet Gateway
In a world where cloud technology is at the center of everything, having a secure, scalable, and well-structured network is essential. The hub-spoke topology in Azure is a great way to manage network traffic efficiently, connecting shared services in a central hub with various workload environments in separate spokes. This guide explores how to set […]
Securing Nginx Ingress with Cert-Manager using HTTP-01 Method
Introduction Securing Kubernetes workloads with TLS certificates is crucial for protecting data and ensuring trust. Cert-Manager automates certificate management, and when combined with NGINX Ingress Controller, it enables easy HTTPS setup using the HTTP-01 challenge. In this blog, we’ll go through the steps to set up Cert-Manager with NGINX Ingress using the HTTP-01 challenge to […]
Centralized Security in AWS Organizations to Managing Multi Account Risks
Managing security and compliance across multiple AWS accounts can be challenging, especially when each account represents a different product, environment, or team structure. While isolating environments (such as production, staging, and development) in separate accounts improves security by limiting lateral movement, it also creates operational complexity. This post explores how to centralize security using native […]
Enforcing Kubernetes Policies with Open Policy Agent (OPA) and Policy-as-Code
Introduction Kubernetes offers a flexible and scalable platform for deploying applications, but enforcing security, compliance, and governance policies across a cluster can be challenging. Open Policy Agent (OPA) addresses this challenge by enabling policy-as-code enforcement within Kubernetes. In this blog, we’ll explore how to use OPA and the Gatekeeper project to define, enforce, and manage […]
How to Securely Connect to EC2 Instances Using AWS Session Manager
In today’s cloud computing environment, security is a top priority. One of the most common challenges when working with Amazon EC2 instances is ensuring secure and controlled access to them. Traditionally, administrators use SSH (for Linux instances) or RDP (for Windows instances) to manage EC2 instances. However, these methods can expose instances to various security […]
Proactively Detect Critical Threats and Strengthen Kubernetes Security with Falco
What is Falco? Falco is an open-source security tool for Kubernetes designed to detect and alert on unusual behavior within a cluster. Initially developed by Sysdig, Falco monitors system activities in real-time and provides alerts for suspicious events. Its flexibility allows users to create custom rules to monitor various aspects of their containerized environments. Falco […]
Enhancing Container Security in the CI/CD Pipeline with Amazon Inspector
Continuous integration and delivery (CI/CD) pipelines are essential for speeding up development and deployment procedures in contemporary software development. However, protecting these containers from vulnerabilities has grown crucial as containerized applications proliferate. In this situation, Amazon Inspector can be quite helpful in improving security in the CI/CD pipeline, especially for images stored in the Elastic […]
Still Leaking Secrets in Git? Let’s Fix This Before It’s Too Late
Common Risks of Hardcoded Secrets in Repositories To mitigate the risks mentioned above, many version control platforms have implemented robust security features designed to prevent secret leaks and enhance the overall security of code repositories. Below is the explanation of security features available on platforms like GitHub, GitLab and Bitbucket, which can help prevent secret […]