Enforcing Kubernetes Policies with Open Policy Agent (OPA) and Policy-as-Code
Introduction Kubernetes offers a flexible and scalable platform for deploying applications, but enforcing security, compliance, and governance policies across a cluster can be challenging. Open Policy Agent (OPA) addresses this challenge by enabling policy-as-code enforcement within Kubernetes. In this blog, we’ll explore how to use OPA and the Gatekeeper project to define, enforce, and manage […]
Storing Helm Charts and Archiving Old Versions to S3: A Practical Approach to Reliability
Introduction Helm is like the app store for Kubernetes—making it incredibly easy to package, deploy, and manage even the most complex applications. When paired with Amazon Elastic Container Registry (ECR), you get a secure and scalable way to store and distribute your Helm charts, ensuring smooth deployments across different environments. But what about old versions? […]
Proactively Detect Critical Threats and Strengthen Kubernetes Security with Falco
What is Falco? Falco is an open-source security tool for Kubernetes designed to detect and alert on unusual behavior within a cluster. Initially developed by Sysdig, Falco monitors system activities in real-time and provides alerts for suspicious events. Its flexibility allows users to create custom rules to monitor various aspects of their containerized environments. Falco […]
Boost Kubernetes security with 3 command line tools
Introduction Kubernetes security can be daunting, given the complexity and multitude of components that need to be protected. From securing the API server to ensuring the integrity of your container images, there are numerous attack vectors that malicious actors can exploit. This is where specialized command line tools come into play, providing powerful capabilities to […]
Blue-Green Deployment Strategy: Essential Kubernetes Progressive Delivery with Argo Rollouts
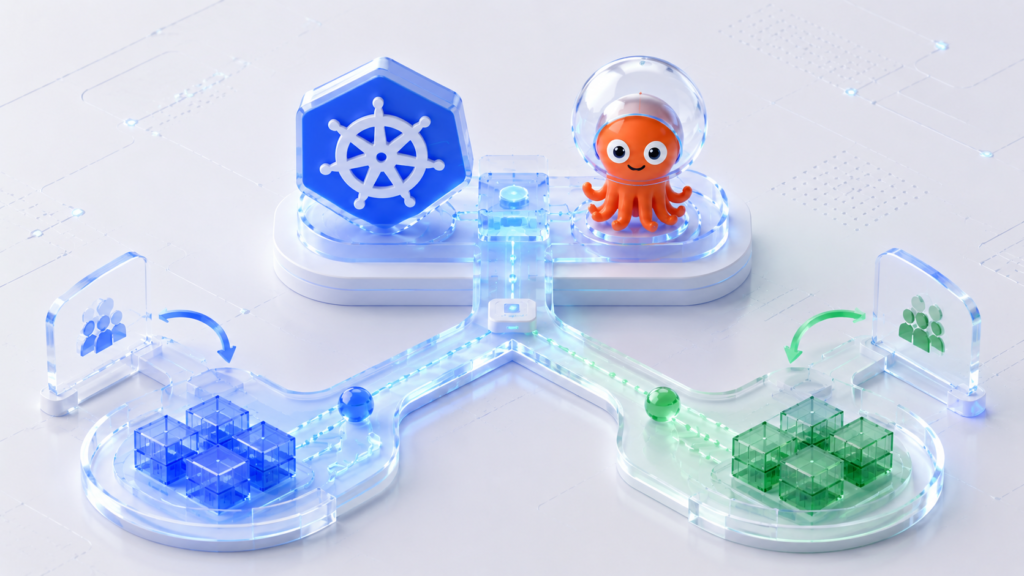
What is Argo Rollouts? A Rollout is a type of Kubernetes workload resource that functions similarly to a Kubernetes Deployment object. It is designed to replace a Deployment in situations where more sophisticated deployment or progressive delivery capabilities are required. A Rollout offers several features that a standard Kubernetes Deployment does not provide: Progressive Delivery […]
Kubernetes Progressive delivery with Argo Rollouts Canary Deployment
In the dynamic world of modern software development, continuous deployment and high availability are crucial. Argo Rollouts are tools that facilitate these goals. In this blog, we’ll explore what Argo Rollouts is, the benefits of using Argo Rollouts, and how to implement a Canary deployment using Argo Rollouts. What is Argo Rollouts? A Rollout is […]
Ingress Nginx with ALB on EKS: Let’s clear this mess and make things easier
When deploying applications on Amazon EKS, many developers prefer to expose using the Application Load Balancer (ALB) due to its robust security features, integrated routing capabilities, and native support for modern web-based applications. ALB stands out with features like path-based routing, SSL termination, and seamless integration with AWS Web Application Firewall (WAF), offering a comprehensive […]
Cost-Effective Dynamic Scaling for AI Workloads on AWS EKS
In this day and age, when AI governs everything, being agile with workload management has become crucial to guarantee peak performance and cost-effectiveness. The need for dynamic scaling solutions that optimize infrastructure utilization efficiently without driving up costs becomes increasingly prominent as demand continues to fluctuate. Kubernetes, indeed, acts as a powerful framework for managing […]
Building a Highly Available Keycloak Architecture with Reverse Proxy
Introduction Keycloak is an open-source identity and access management solution that provides single sign-on (SSO), identity brokering, and user federation. When deploying Keycloak in a Kubernetes environment, it is crucial to ensure that the data stored in both Keycloak and its backing PostgreSQL database remains persistent even if the pods are restarted or deleted. This […]
Managing Kubernetes Secrets with AWS Secrets Manager and External Secrets Operator
What is External Secret Operator? External Secrets Operator is a Kubernetes operator that integrates external secret management systems like AWS Secrets Manager, HashiCorp Vault, Google Secrets Manager, Azure Key Vault and many more. The operator reads information from external APIs and automatically injects the values into a Kubernetes Secret. Instead of storing sensitive information directly […]